Upgrade the MCP TypeScript SDK now if your application uses HTTP transports, OAuth, or the experimental task store. Releases 2.3.0 and 1.32.0, published on October 2, 2026, stop cross-origin redirect leaks and prevent clients from accessing tasks created by another session.
Model Context ProtocolMCPA standard that lets an AI program use your tools and data under clear permissions.Open the glossary, or MCP, is an open protocol that connects AI applications to tools, data, and external services through consistent contracts. Its official TypeScript SDK provides clients, servers, Streamable HTTP and SSE transports, and OAuth helpers.
What does MCP TypeScript SDK 2.3.0 fix?
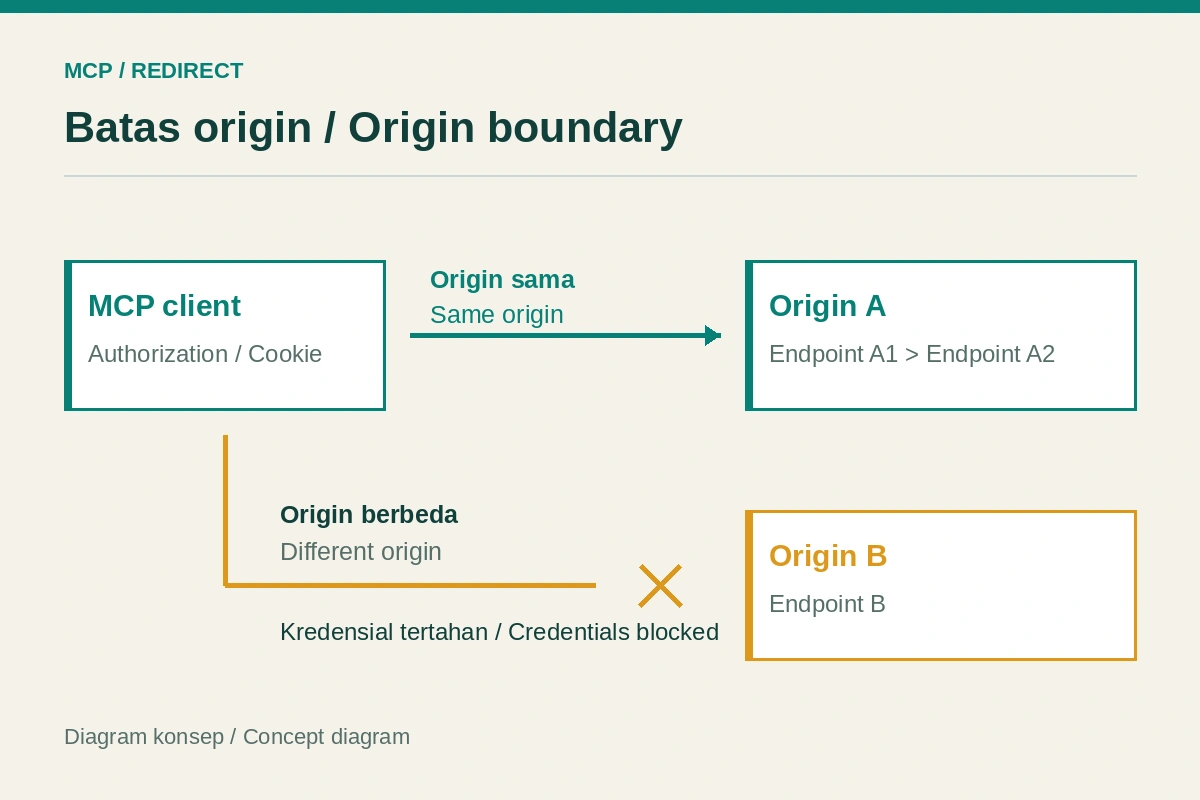
The official GHSA-6prh-2h8m-c8cw advisory, published October 2, 2026, says HTTP client transports and OAuth functions could follow redirects to another origin. The destination could receive custom headers, the mcp-session-id header, and request bodies on HTTP 307 or 308 redirects. An OAuth body can contain a refresh_token and client_secret.
The fix in @modelcontextprotocol/client 2.3.0 limits automatic redirects to the same origin. The 1.x line has the same fix in @modelcontextprotocol/sdk 1.32.0. Browsers no longer follow these redirects by default.
Is your MCP application affected?
| Component | Affected versions | Safe version | Impact |
|---|---|---|---|
| 1.x SDK | All versions through 1.31.0 | 1.32.0+ | Cross-origin redirects can forward sensitive data |
| 2.x client | 2.0.0-2.2.0 | 2.3.0+ | HTTP transports and OAuth are affected |
| Experimental task store 1.x | 1.24.0-1.31.0 | 1.32.0+ | Another session can read or cancel tasks |
| 2.x task packages | Not affected by the task advisory | Use the latest version | The redesigned task system is separated |
The redirect risk applies when an application uses StreamableHTTPClientTransport, SSEClientTransport, or OAuth functions such as auth(). Stdio clients are not affected by this redirect advisory.
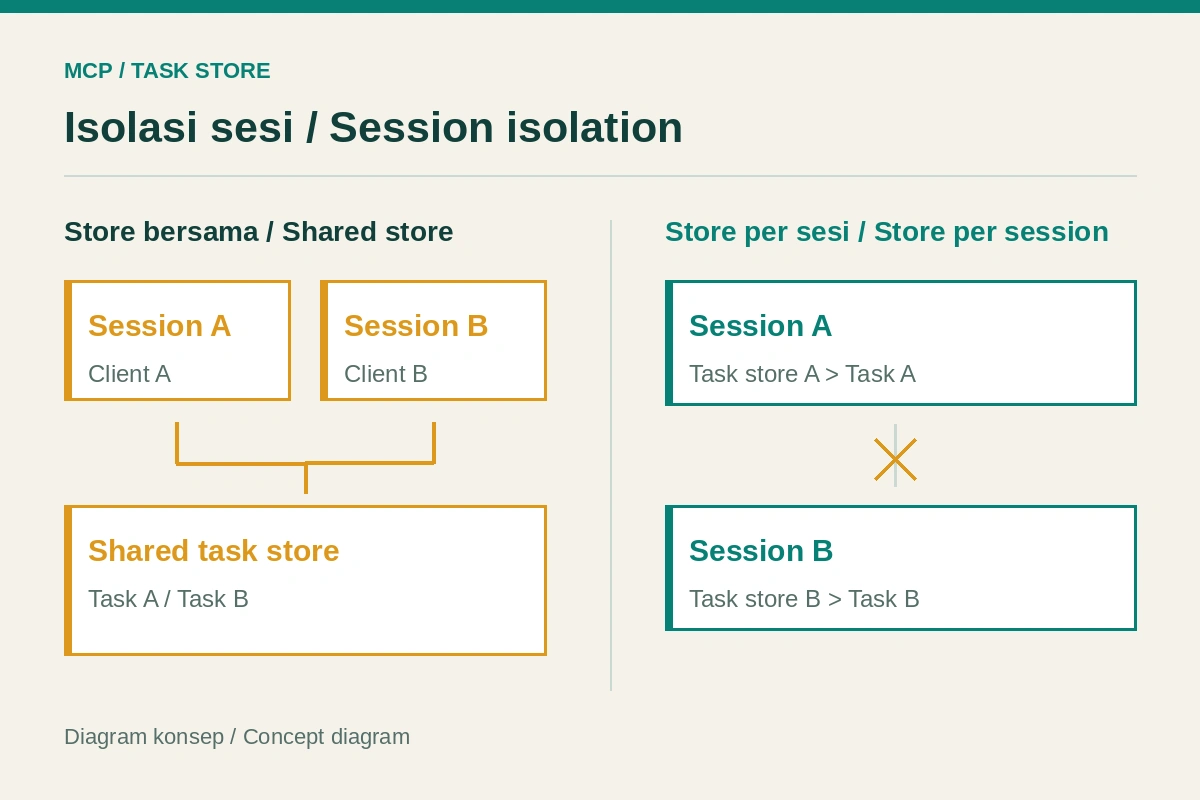
The second advisory, GHSA-22jm-h49p-29qw, also dated October 2, 2026, applies when a 1.x server passes taskStore to McpServer or Server. Clients that shared one InMemoryTaskStore could list, read, or cancel tasks from another session. The MCP 2026-07-28 specification deprecated this experimental feature.
What can break if you do not upgrade?
The application does not necessarily stop. This makes the issue harder to detect. A misconfigured, malicious, or compromised server can redirect a request to another host. Custom credentials and session tokens can then leave the expected boundary without a clear error.
On a multi-tenant server that uses the experimental task store, one client can reach another client's tasks. The result can include leaked work results, cancelled jobs, and lost tenant isolation.
How do you upgrade safely?
- Inventory packages with
npm ls @modelcontextprotocol/sdk @modelcontextprotocol/client. - Upgrade the 1.x line to
@modelcontextprotocol/sdk 1.32.0or later. Upgrade the modular 2.x client to@modelcontextprotocol/client 2.3.0or later. - Find each use of
taskStore. Remove the old experimental feature when possible. Otherwise, use one store for each session. - Test MCP endpoints that redirect to another host or port. Configure the final URL. Do not restore
redirectPolicy: 'follow'without a risk review. - If logs show redirects to a host that you do not control, rotate APIAPIThe official door 2 systems use to exchange data, without anybody copying it by hand.Open the glossary keys and the
client_secret. Revoke the related tokens. - Run regression tests for OAuth, SSE reconnects, and Streamable HTTP requests before production rollout.
Release 2.3.0 also changes stateless server use. Do not share one server or transport instance across all requests. Create the McpServer and transport in the request handler. Otherwise, the second request can fail with ALREADY_CONNECTED or HTTP 500. The official 2.3.0 release notes document this upgrade requirement.
Operational decision
Prioritize this upgrade today for deployments that use HTTP transports or OAuth. A stdio-only deployment without a task store is not directly exposed to these advisories. It still needs a planned update because 2.3.0 changes the server lifecycle.
Teams that also use Python can read our MCP Python SDK 2.3.0 checklist. For integration and agentAI agentAn AI program that performs work steps by itself, for example reading a message, drafting a reply, and recording the result.Open the glossary guardrail reviews, see Rama Digital AI and automation services.
Questions and answers
Must every MCP user upgrade?
TypeScript SDK users with HTTP, SSE, OAuth, or the old task store should prioritize the update. Stdio clients are not affected by the redirect advisory.
Which versions fix the issues?
Use @modelcontextprotocol/sdk 1.32.0 or later for 1.x. Use @modelcontextprotocol/client 2.3.0 or later for the modular 2.x line.
Can I enable cross-origin redirects again?
Yes, with redirectPolicy: 'follow'. This restores the old behavior and its exposure. Using the final endpoint URL is safer.
What if credentials might have leaked?
Rotate API keys and client secrets. Revoke tokens, inspect egress logs, and make sure the final endpoint no longer redirects to another origin.